Managing S/MIME certificates and PGP keys
Manage S/MIME certificates and PGP keys centrally: import, issue through SwissSign or your own MPKI, issue and renew S/MIME certificates and PGP keys per group automatically, distribute over LDAP.
SecureMail manages all certificates and keys centrally in the tenant. Public certificates of the counterparts and your own private certificates are held separately and are available to the routing for signing, encrypting, decrypting and signature verification.
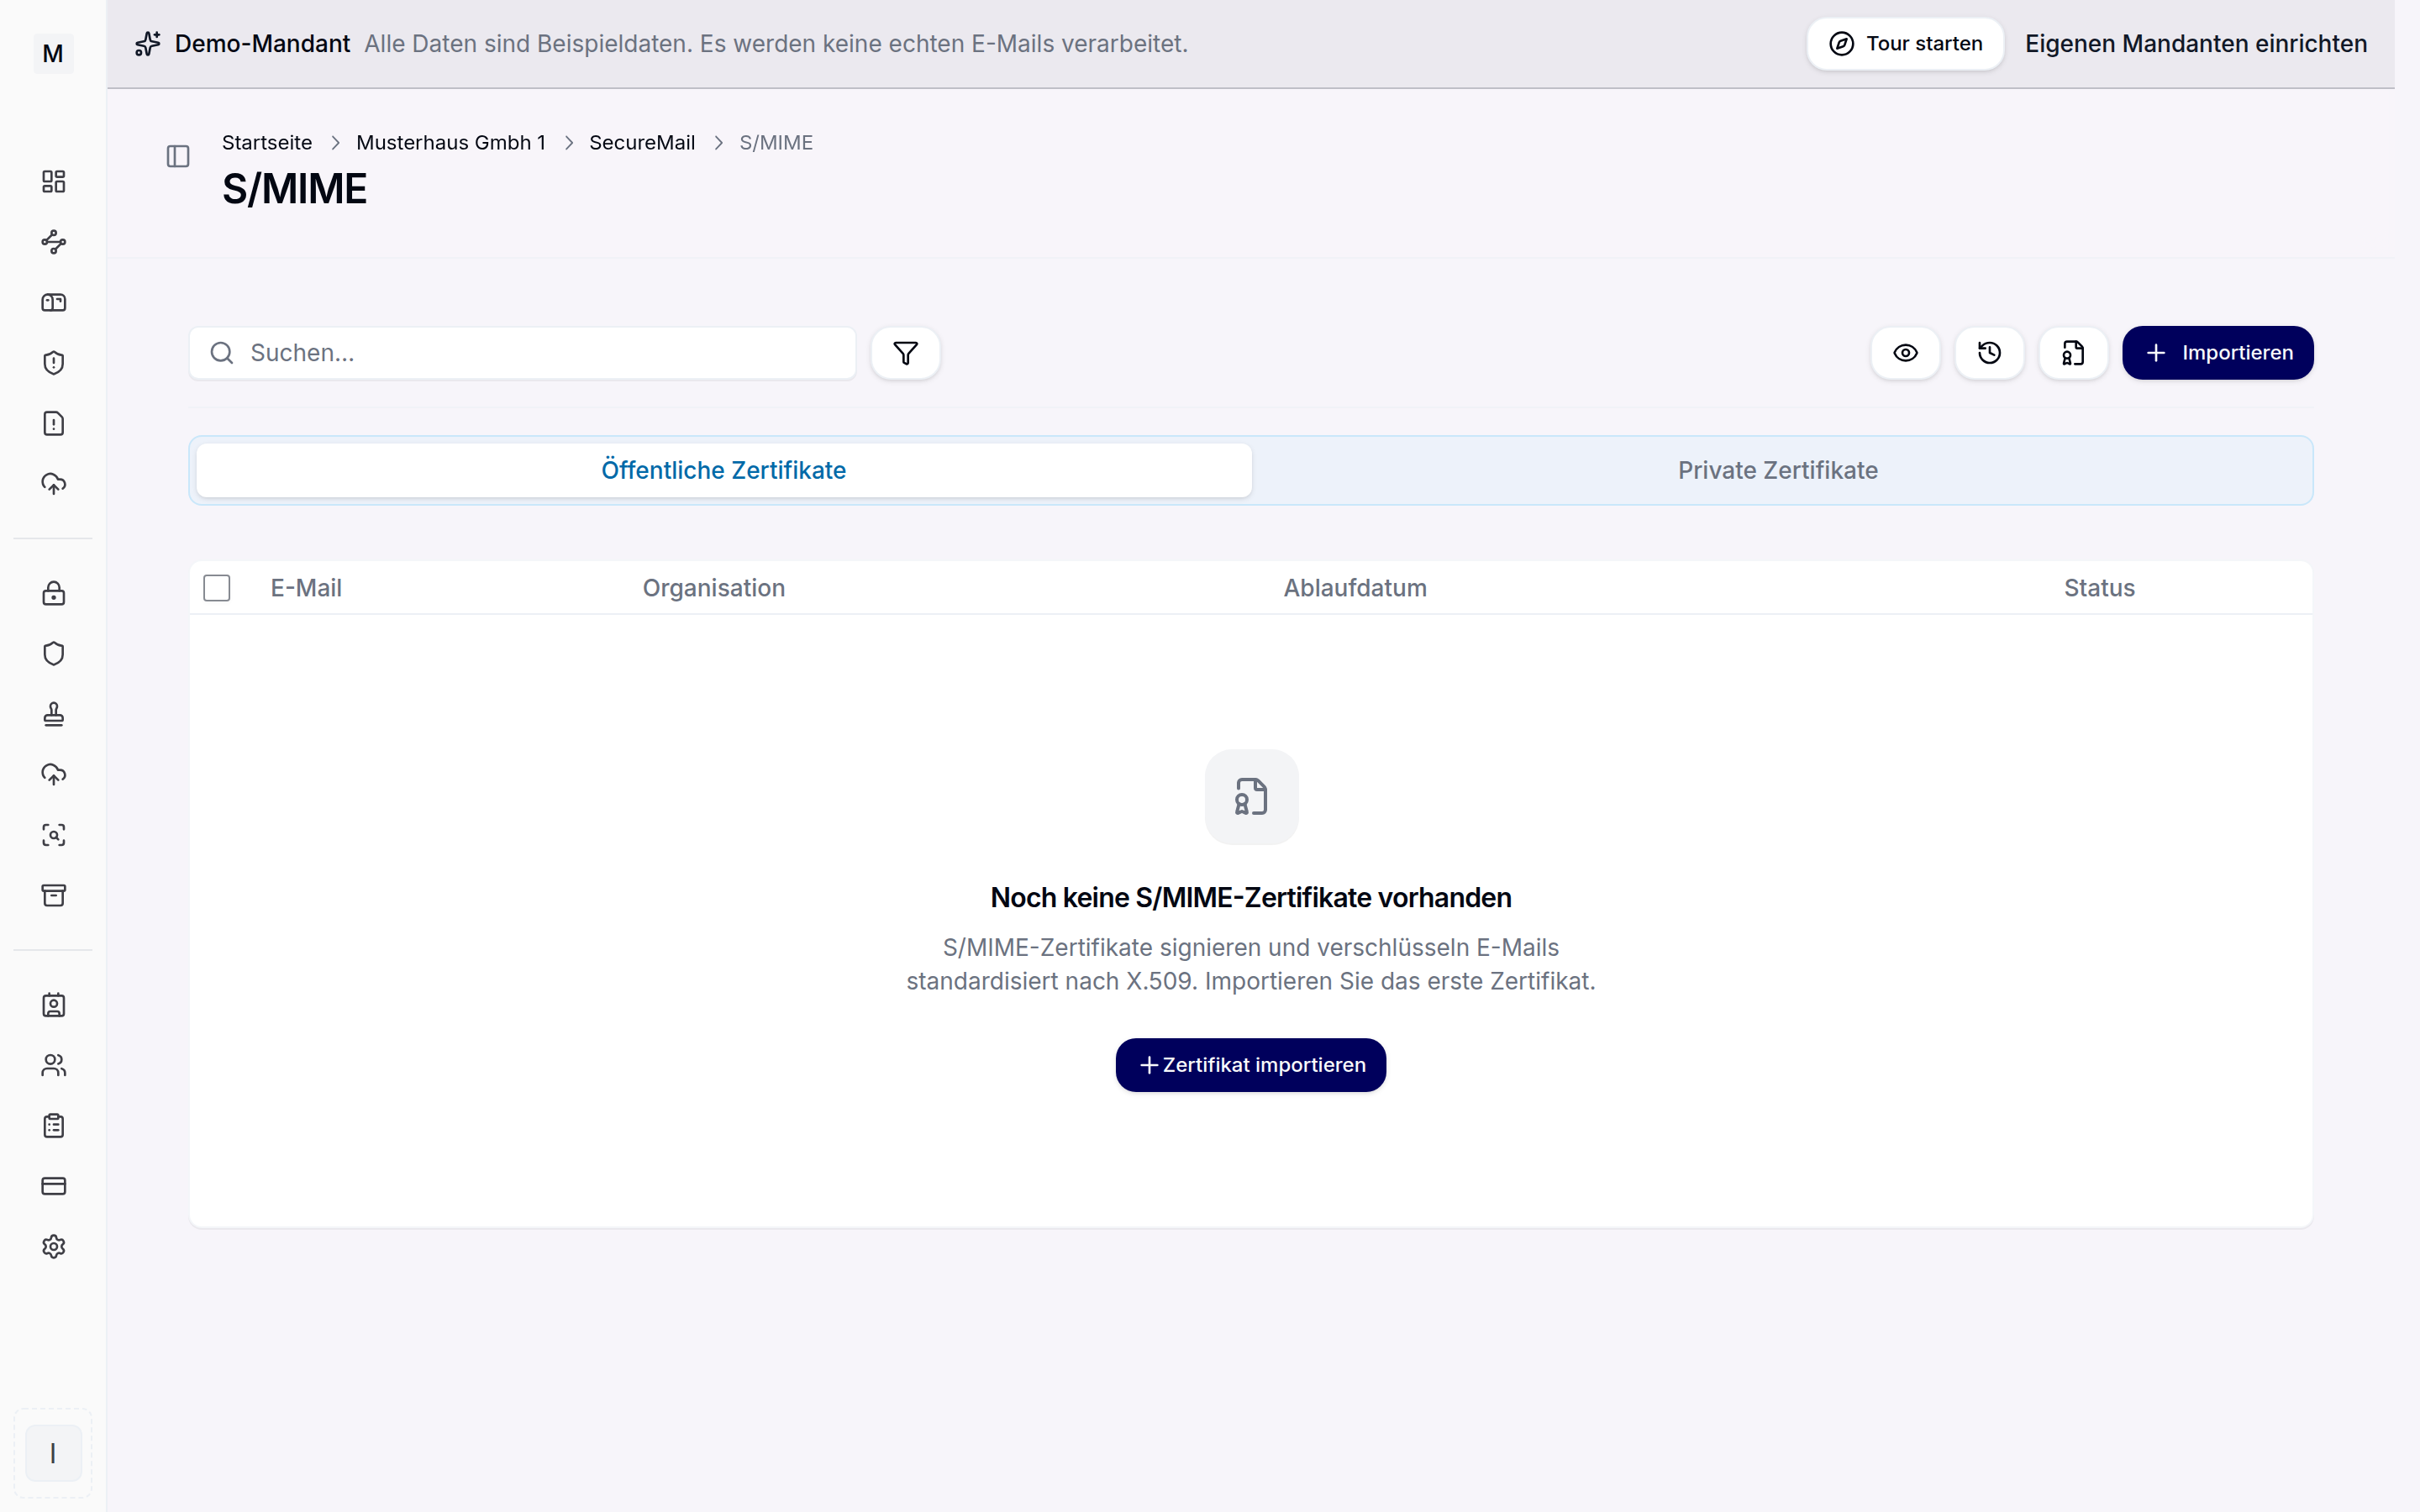 Central management of the S/MIME certificates.
Importing certificates and keys
S/MIME certificates can be imported from a file, the formats crt, pem, der, p7b, p7c, p12 and pfx are supported. PGP keys are read in as gpg, pgp or asc. Private keys can additionally be held in a hardware security module. Existing certificates can be viewed and downloaded, for instance for export into other systems.
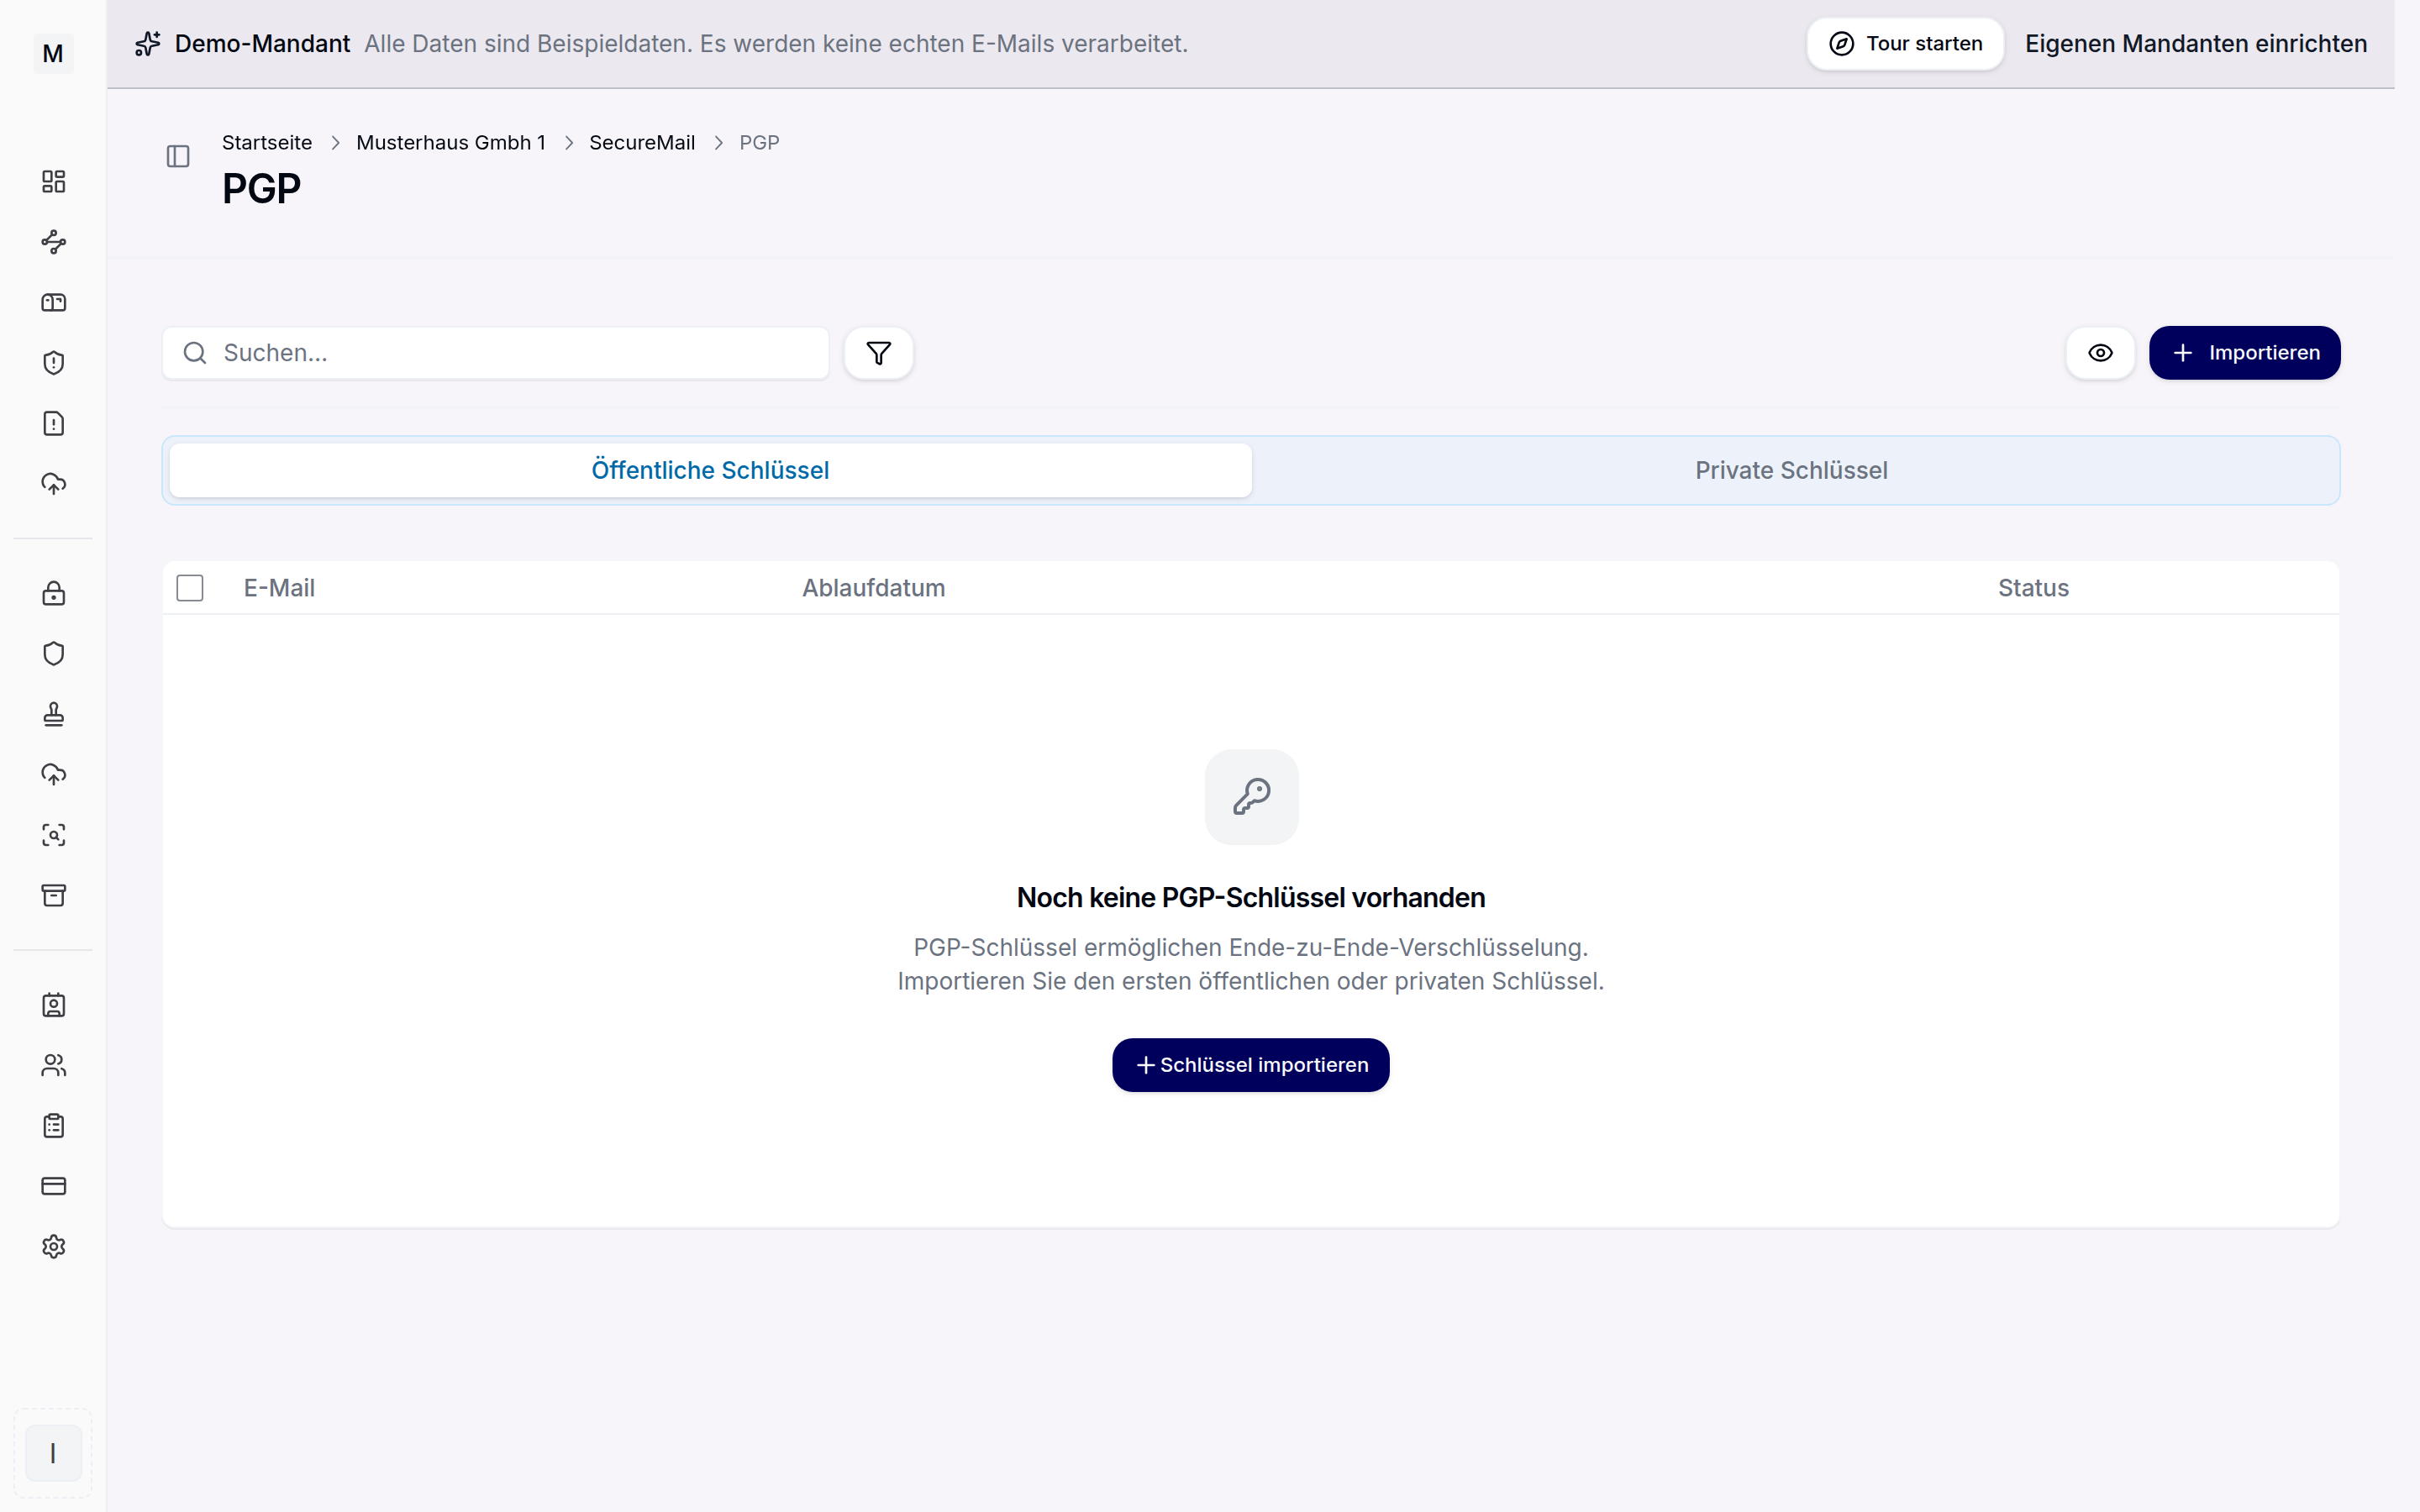 Management of the OpenPGP keys.
Issuing certificates through SwissSign or your own MPKI
Besides importing, SecureMail can issue certificates itself. Through the SwissSign connection, publicly trusted S/MIME certificates are ordered from a trust centre. Alternatively your own MPKI, that is an internal certificate authority, issues certificates for your own mail addresses. The internal CA suits infrastructures without an external provider.
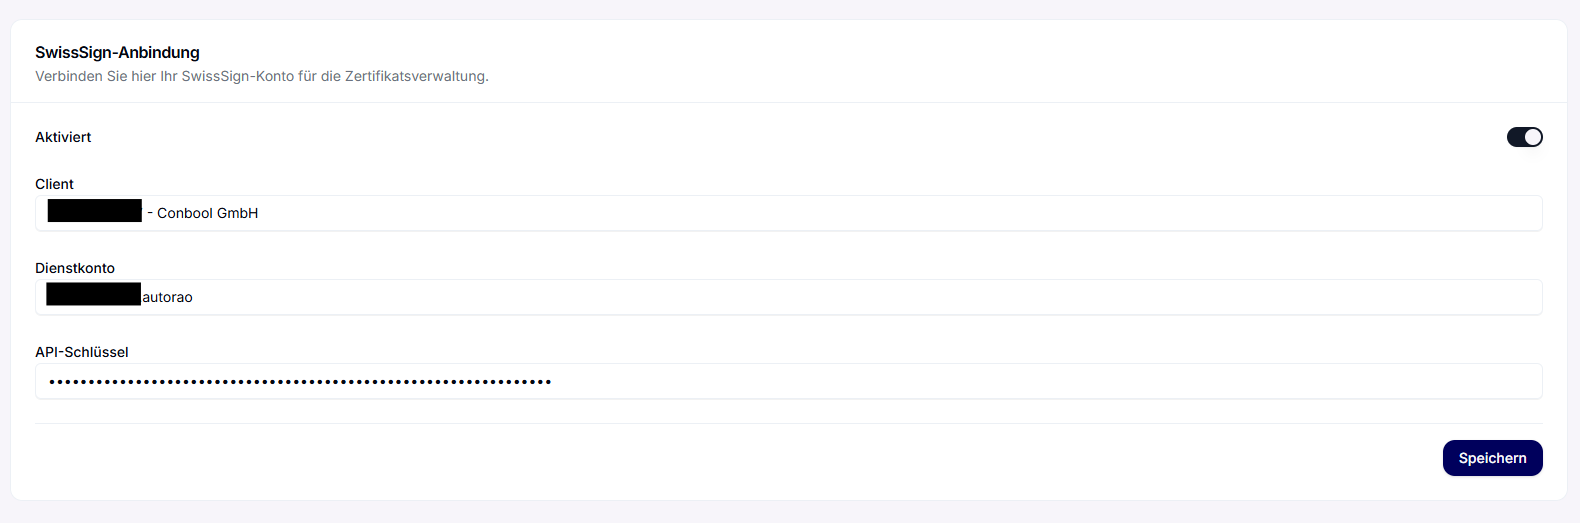 Choosing the certificate authority, SwissSign or your own MPKI.
Automatic renewal
Automatic renewal checks daily for certificates about to expire and renews them in time. It is available for certificates of the internal CA and for certificates issued through SwissSign and is switched on per domain under Settings › SecureMail › Certificates. The same page sets how many days before expiry a certificate is renewed, 7 days by default. Certificates of members of a group with S/MIME issuance are renewed even when the domain has renewal switched off. In addition, advance notifications warn before the expiry date. Individual certificates can be renewed or revoked manually.
Automatic S/MIME certificates for groups
For a group, SecureMail can issue an S/MIME certificate to every member, through SwissSign or the internal CA. The Issue certificates switch is under Administration › Groups in the group, on the S/MIME certificates card. Below it you choose the provider and the SwissSign product, or the internal CA with its validity.
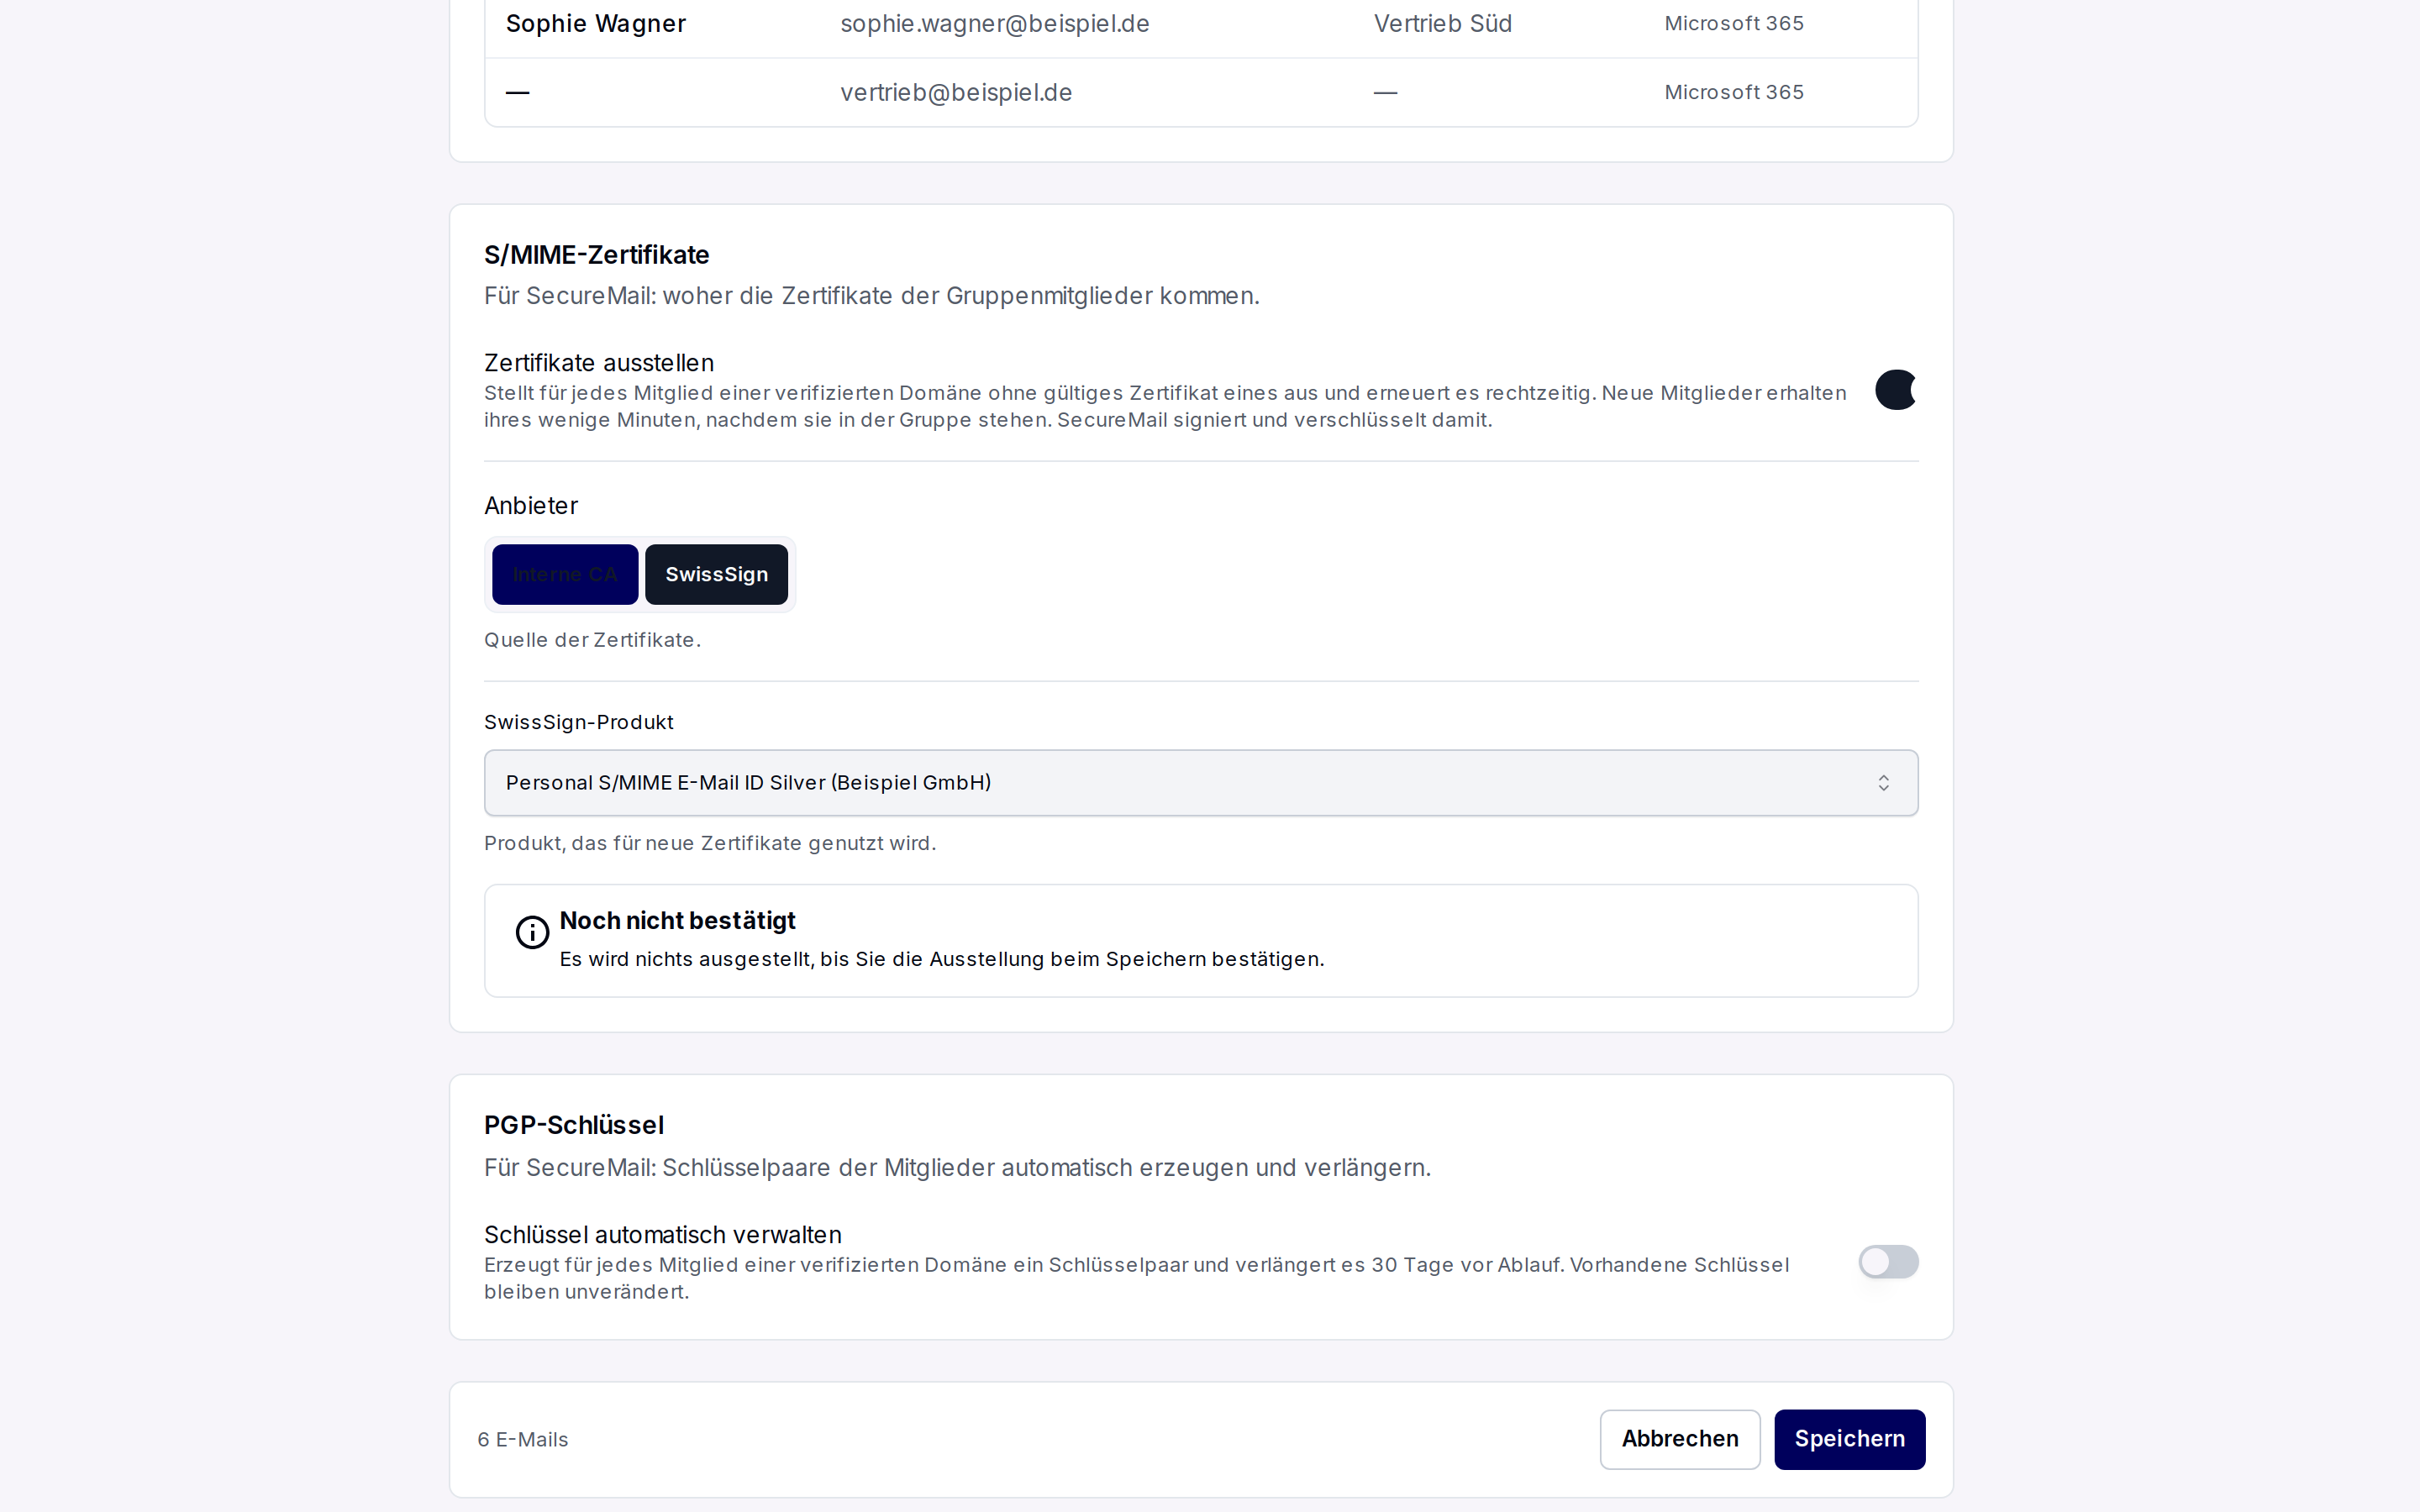 Switched on but not yet confirmed: nothing is issued yet.
- Confirm: when you save with the switch on, SecureMail asks whether to issue and shows the number of members. Only Issue and save places orders. Save only keeps the setting without issuing anything. Changing the provider, product or CA requires a new confirmation. Confirming requires the same permission as issuing certificates manually.
- Issue: every member with an address on a verified domain who has no valid certificate yet receives one. Existing certificates stay, whether imported, ordered manually or issued automatically. Addresses on other domains and distribution list addresses are skipped.
- New members: when a member is added, manually or through the directory sync, they receive their certificate a few minutes later. After saving or refreshing the group, issuance starts immediately.
- Renew: automatic renewal renews the members' certificates in time before they expire. If someone leaves the group, their certificate stays valid; it is then only renewed if the domain has automatic renewal switched on.
- Costs: SwissSign orders go through the tenant's SwissSign account and are billed there. Products that require registration documents are never ordered automatically. If an order is not completed, SecureMail does not order again for that address and shows it in the group instead. No further orders are placed in the same run. After two such orders within seven days, automatic orders for the tenant are paused until the addresses listed have a certificate.
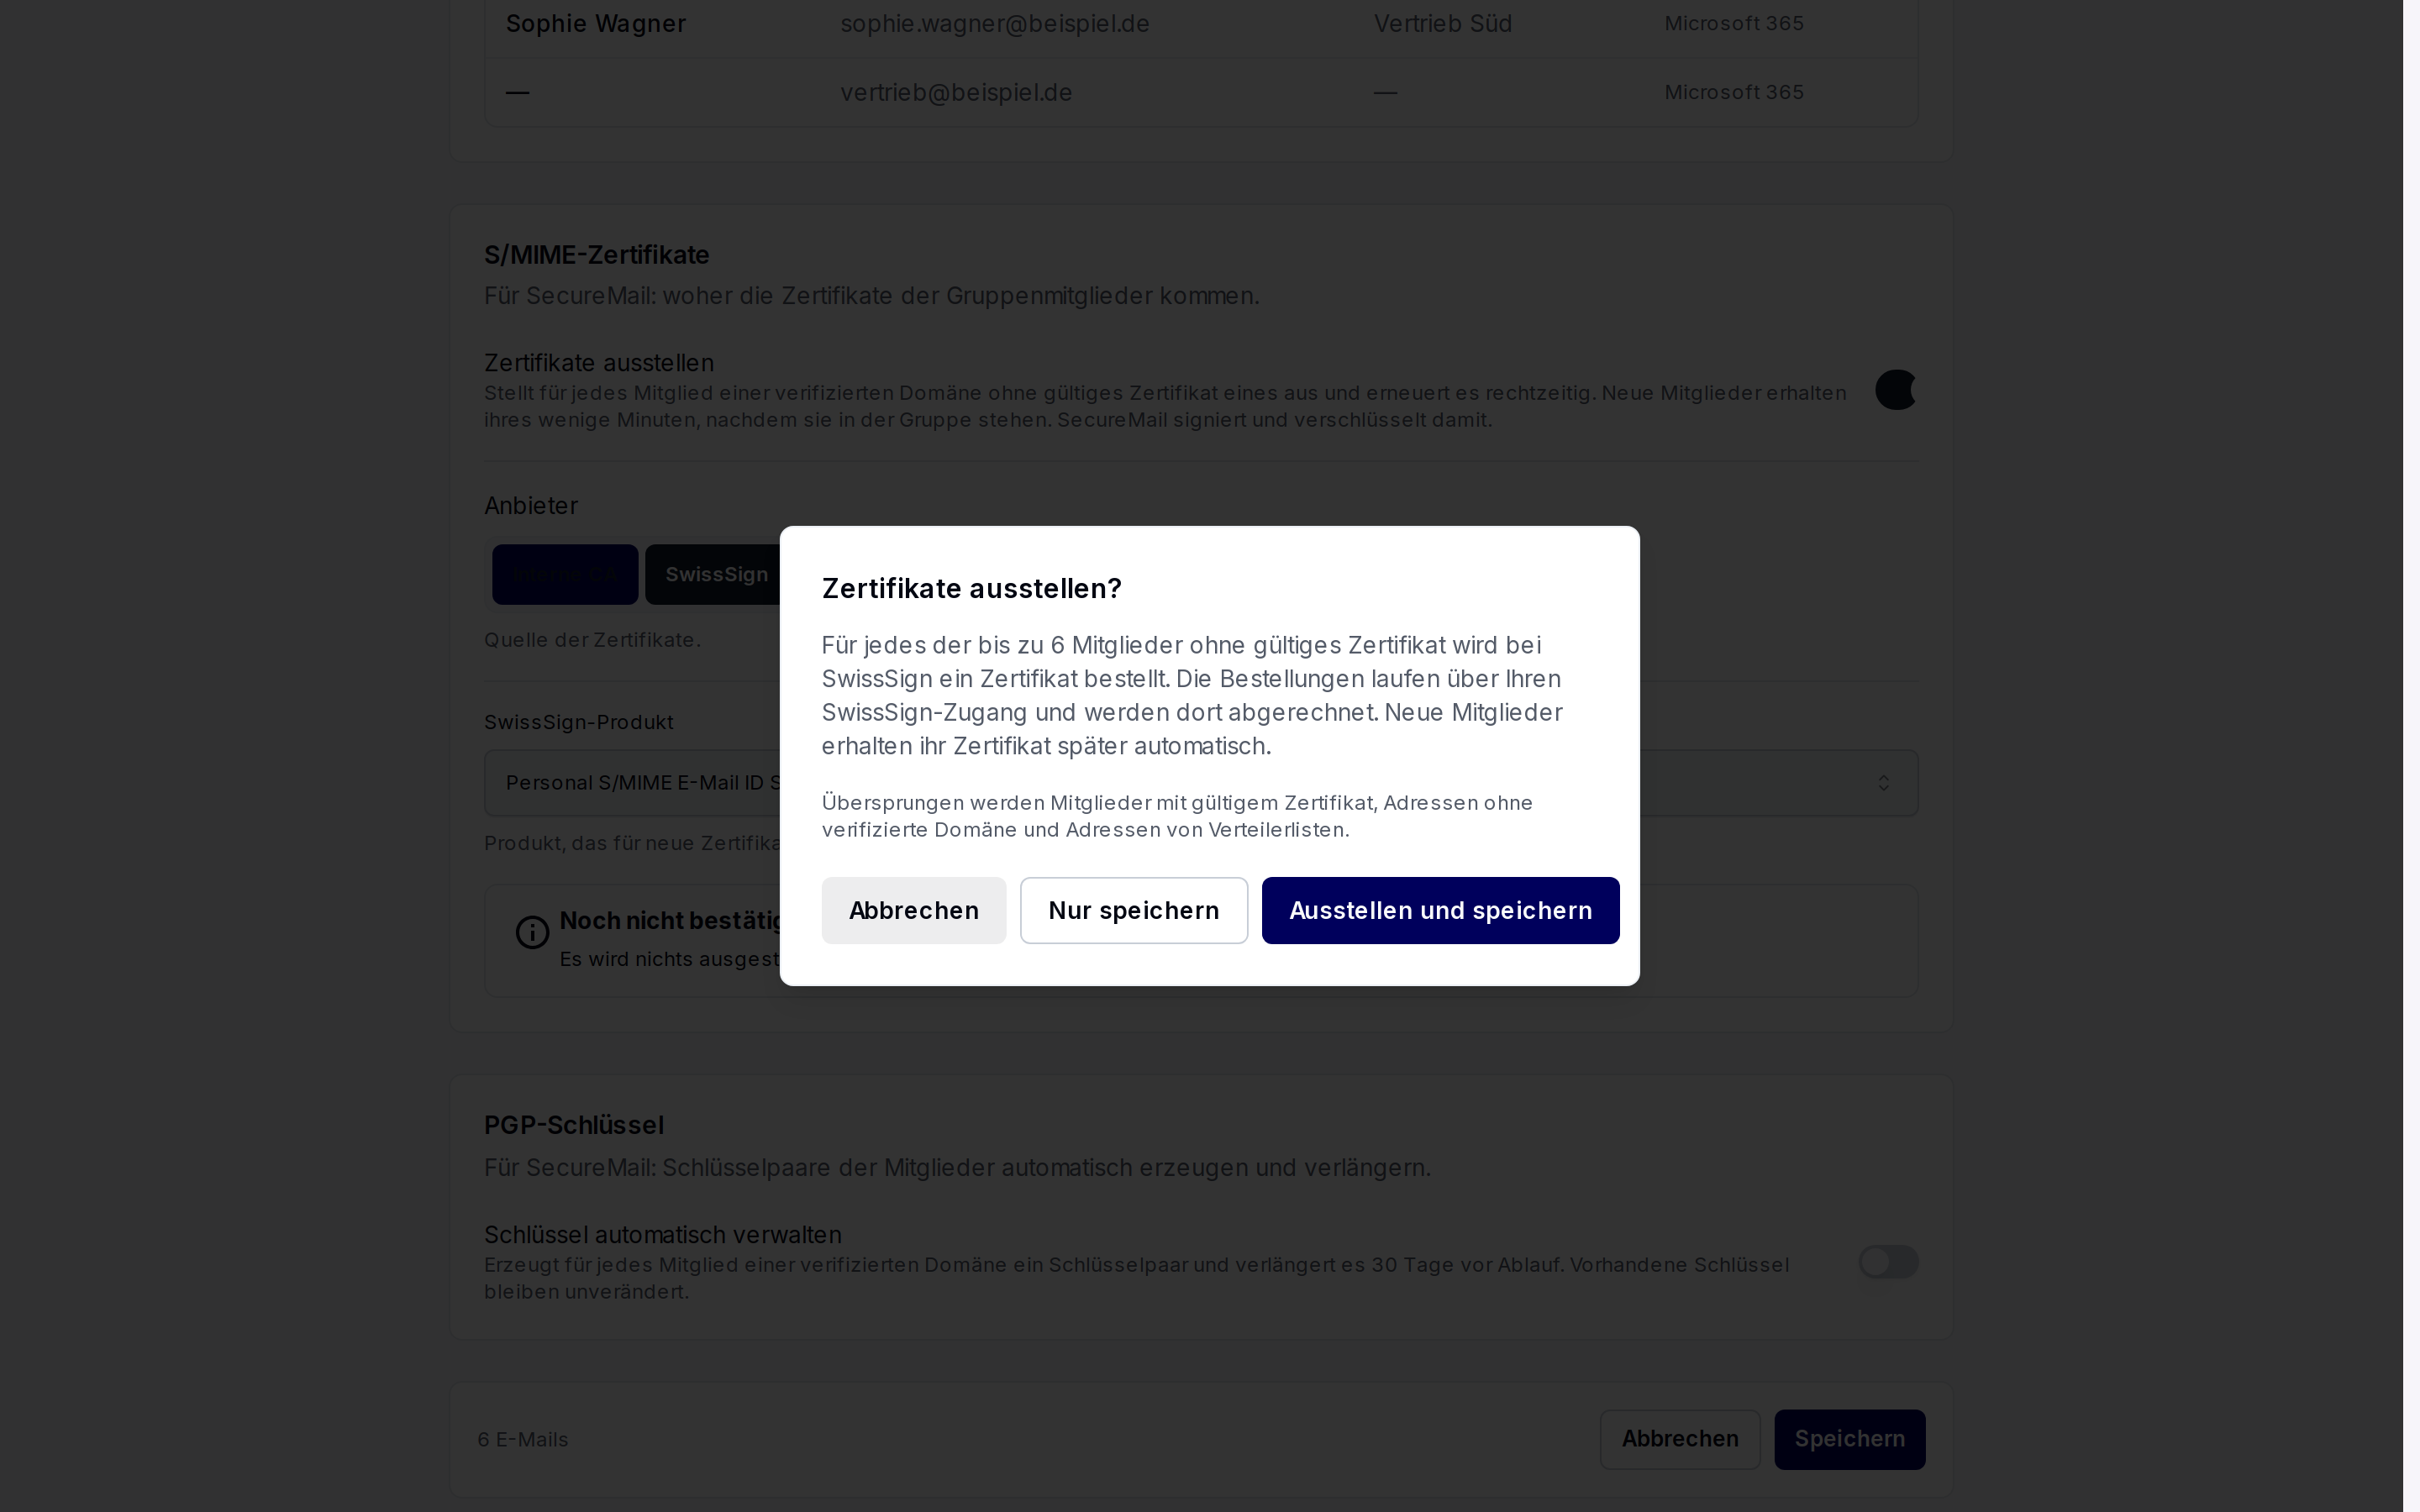 SecureMail asks before the first order.
If an address belongs to several groups with issuance, the settings of the oldest group apply. The card in the group shows the result of the last run: issued certificates, members with a valid certificate, skipped addresses and addresses that need attention. Every issuance is recorded in the log under Settings › SecureMail › Certificates. Issuance requires a SecureMail licence.
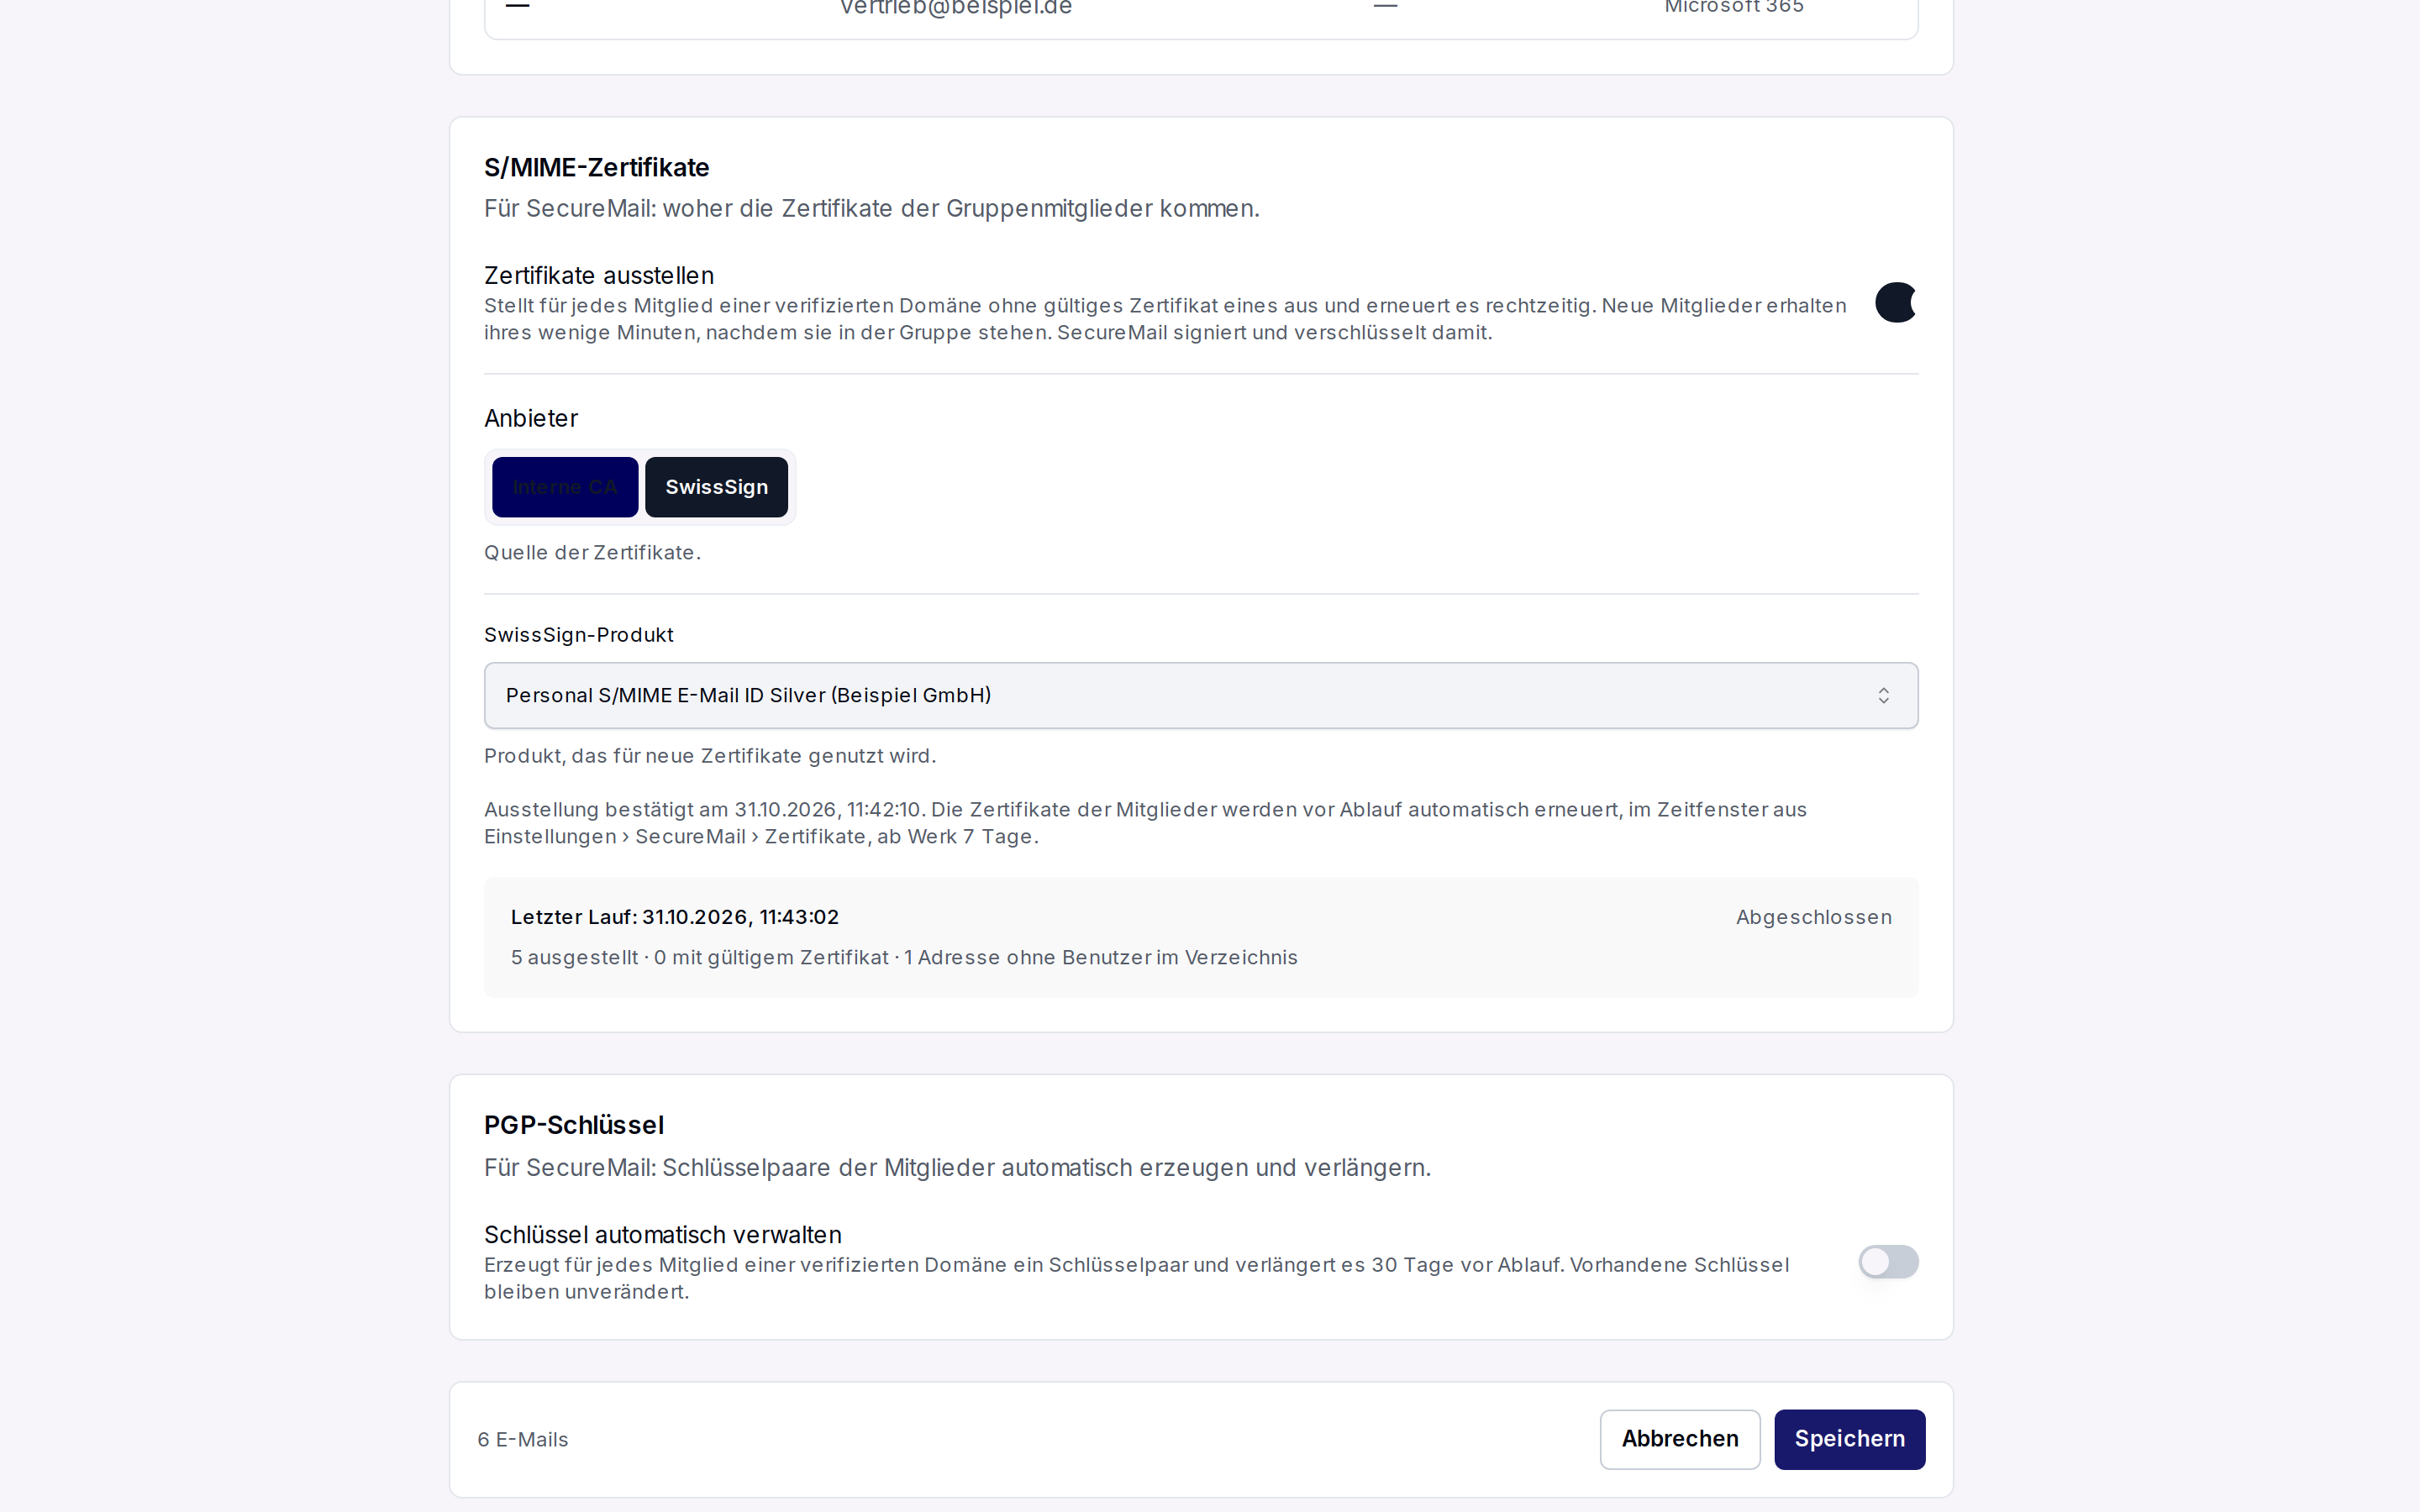 Five certificates issued, the distribution list address skipped.
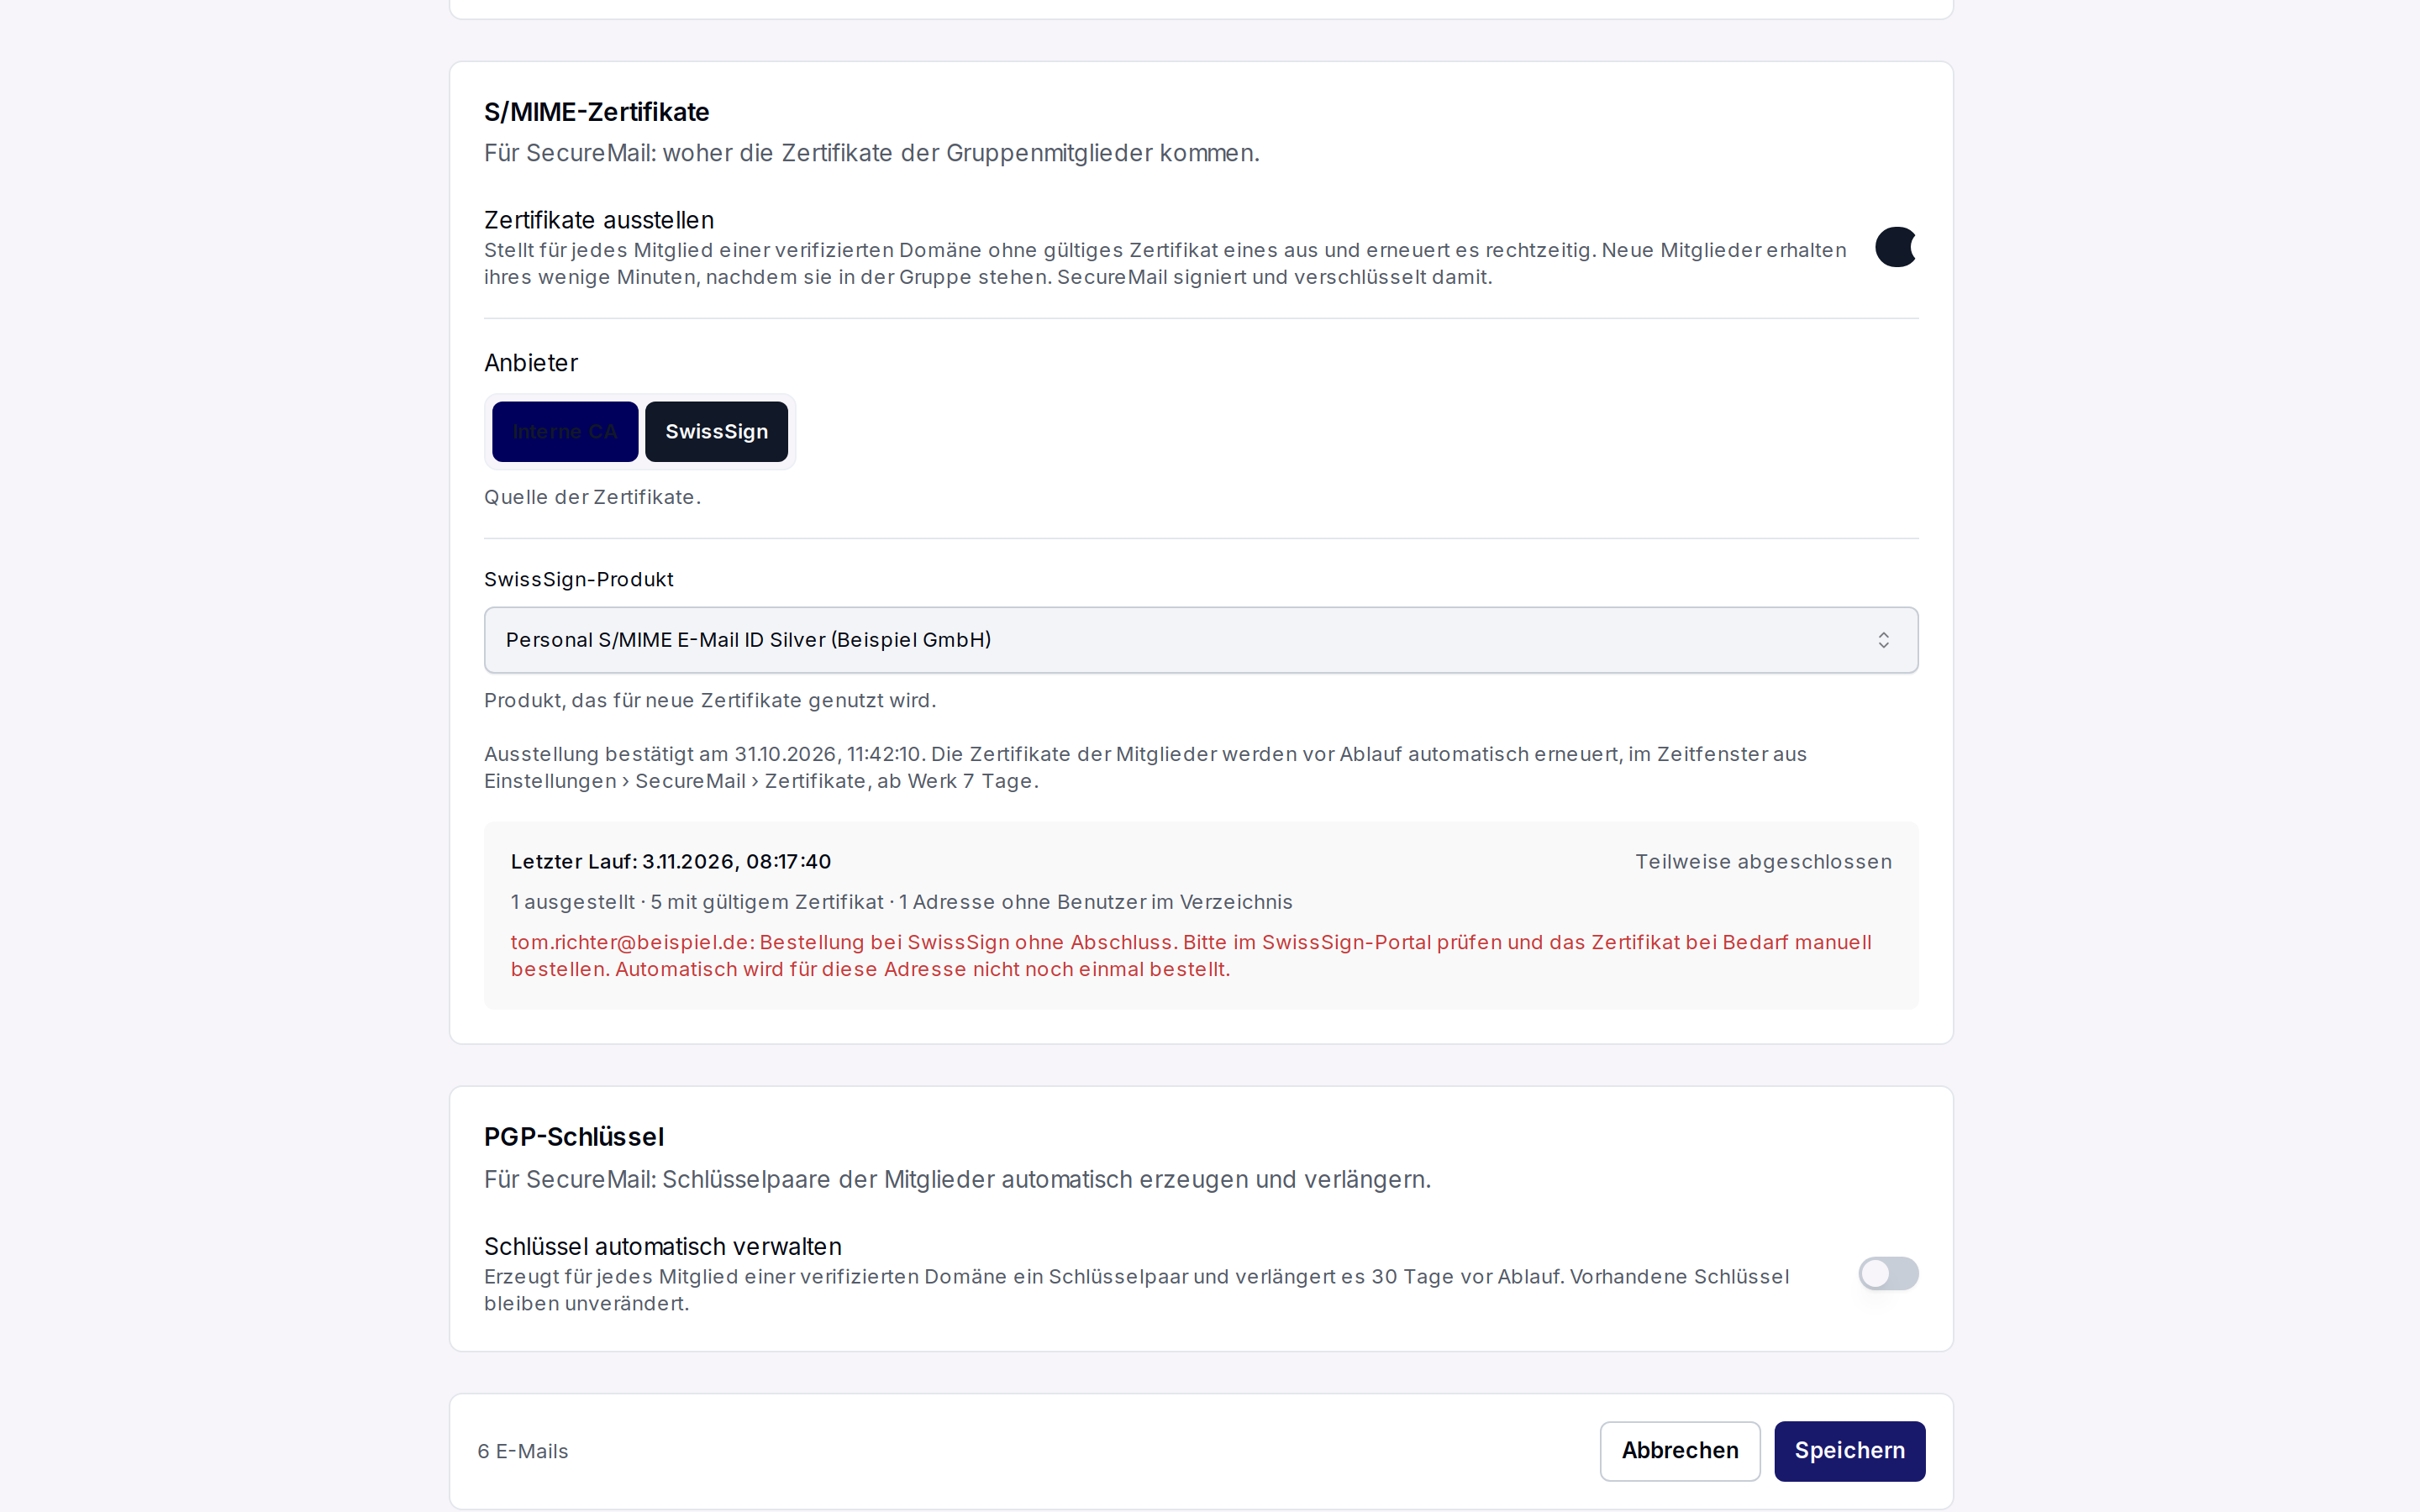 An order without completion: no further order is placed automatically for this address.
Automatic PGP keys for groups
For a group, SecureMail can create PGP key pairs for all members and keep them current. The switch is under Administration › Groups in the group, on the PGP keys card. The same card sets the algorithm for new keys, Ed25519 or RSA 4096, and the validity from one to ten years.
- Creation: every member with an address on a verified domain of the tenant receives a key pair. Addresses on other domains are skipped, because their keys belong to the other party.
- Renewal: 30 days before expiry, SecureMail extends the key by the configured validity. The key stays the same and its fingerprint does not change. Correspondents only need to re-import the public key instead of trusting a new one.
- Existing keys: imported keys and keys created manually are never changed by the automation. If such a key expires, the group shows a notice.
- Timing: the run starts right after the group is saved and then every hour. New members therefore usually receive their key within an hour. When very many keys are due at once, SecureMail spreads them over several runs.
If an address belongs to several groups with the automation enabled, the algorithm and validity of the oldest group apply. The card in the group shows the result of the last run: created, renewed and unchanged keys, plus addresses that need attention. A notice appears, for example, when SecureMail would use the key of another address for an address, or when a key pair is incomplete. Every creation and renewal is recorded in the audit log.
An overview is on the PGP key management page. The automation requires a SecureMail licence. Enabling or changing it in a group additionally requires the permission to import PGP keys.
Distribution over LDAP
Through an LDAP connection SecureMail can look up certificates in a directory. A separate base DN for certificates can be stored for this and used as a fallback when no matching certificate is available locally. Central directories and the mail flow thus stay in sync.
How the keys are used in operation is shown in inbound messages and outbound messages. The connection to Entra ID is described in SecureMail for Microsoft 365. The SecureMail index gives an overview.